Our organisation has a fundraising side and a membership side. We use NXT and DBV (hosted solution) as the CRM for our fundraising activity, but we'd also like to use it to hold our member data too.
I want to keep this as separate as possible and have setup separate security groups in DBV for staff who work on the membership side, and I have restricted their access to the 2 membership constituent codes only. In NXT I have also created separate roles for membership accounts.
I've been testing to ensure that membership people don't have access to fundraising supporter data (records that don't have the 2 membership constituent codes) through some of the NXT features.
I've found that membership accounts can see and open lists that select records without those 2 membership constituent codes, but the records don't appear when the records are listed on screen, so that seems good.
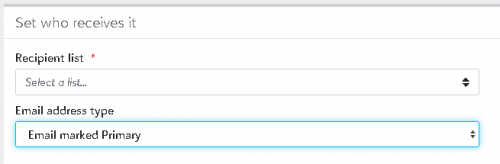
However, I was testing NXT email marketing and I've found that if a list that selects fundraising records was accidently selected as the recipient list for a marketing email, then the email will still get sent to constituents on the list despite the membership account not having access to those records and them not appearing when the list is opened.
Seems to me there is a risk (maybe small) that if membership selected the wrong list, we could email fundraising supporters an email they shouldn't receive.
We don’t use NXT for our fundraising supporter email comms and we’re in the UK, so we need to ensure we are only emailing supporters who have explicitly consented to email marketing.
Seems to me there is a risk (maybe small) that if membership selected the ‘wrong’ list, we could email fundraising supporters an email they shouldn't receive because it was meant for membership and we could actually send to fundraising supporters who haven’t consented to email marketing (we don’t give them an opt out solicit code unless they’ve actually unsubscribed in our mass email tool or contacted us to ask to change their consent).
We can reduce the risk with good user processes and double checking the list selected when sending an email to the membership audience, but I’d rather have a systemic way of reducing this risk too. Does anyone know a way I can do this?